Prove it
Verifiable audit log
Know who did what and when, and be able to check that nobody has touched it since.
What it is for
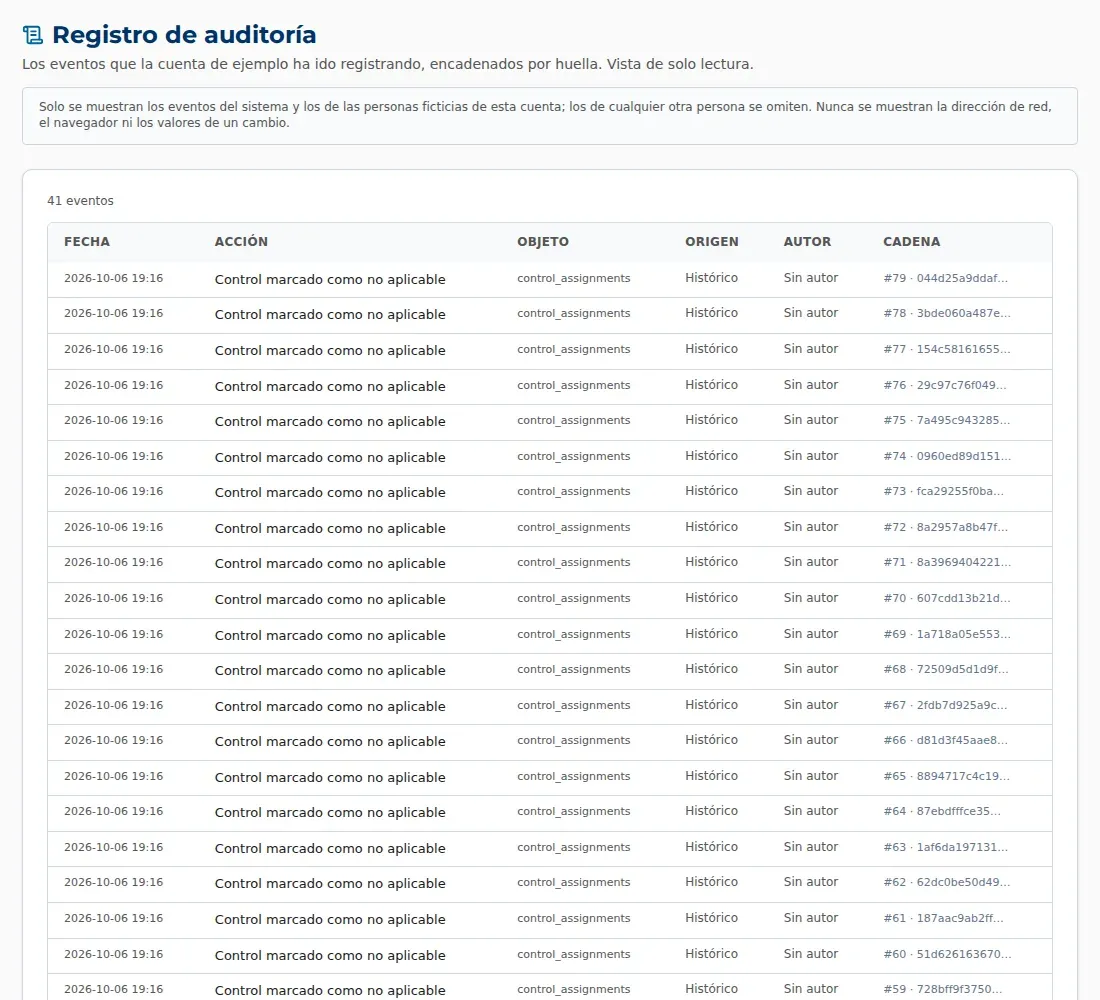
Your organisation's actions are recorded with their author, their time and their hash. Every event carries a SHA-256 integrity hash and is chained to the previous one: it is designed so that any change or deletion of an event already on record would be detected.
What it cannot detect is an event that never got recorded: that is what the write-failure log is for, and we review it daily.
When the author is “Alethexis administrator”, this is an action by the Alethexis team on your organisation. We record it here on purpose: you can see what we did, when and on what.
How it works
A chain checked every day
Each organisation's chain is verified automatically every day, and the result is shown on the log itself. Under “Log integrity” you see the last automatic check and can press “Verify now”: the result is “Intact”, with the number of events verified, or “Alteration detected from event… onwards”.
Anchored outside the database
A database administrator could try; what we offer is that it would be detected. Every day we export the chain heads to a store outside the database, with a different provider and a different access control, and we compare them the following day: a complete reconstruction of the log would be detected.
A viewer with filters
You narrow what you see by dates, family, action, person and source. Each row shows date and time, author, action, object and source; the detail opens the changed fields and the event hash (SHA-256) with its position in the chain.
Who sees it
The Owner, AI Officer, DPO and Auditor, read-only. Only the Owner and the DPO see the previous and new values of each change. An external auditor can review it with a temporary access.
What you get
CSV export
You download what you are looking at, with the filters applied. The export covers up to 5,000 events from the active filter, starting with the most recent.
PDF with integrity hash
A verifiable extract of your organisation's log: it records the filters applied, the events included, the integrity check at the time of issue and the hash of the last event in the range.
FAQ
- Is there anything the log cannot detect?
- Yes: an event that never got recorded. That is what the write-failure log is for, and we review it daily. The chaining is designed so that any change or deletion of an event already on record would be detected.
- What do I do if the check detects an alteration?
- Contact support: this is an incident and we treat it as one.
- Can I see what the Alethexis team does in my account?
- Yes. Its actions appear with the author “Alethexis administrator”: you can see what we did, when and on what.
- How long is the log kept?
- As a general rule, we keep the log blocked for a maximum duration of five years from the end of the engagement, without prejudice to a different limitation period being applicable or to a legal cause interrupting or extending that period.